Tell us what you want to achieve and we’ll get in touch…
Free delivery
Safe and secure checkout
Credit and debit card payments
In: Plixer, Netflow Replication
Plixer FlowPro DNS Analytics and Deep Packet Inspection 1 year of 3-year subscription
Product code: PLX-FP-3Y
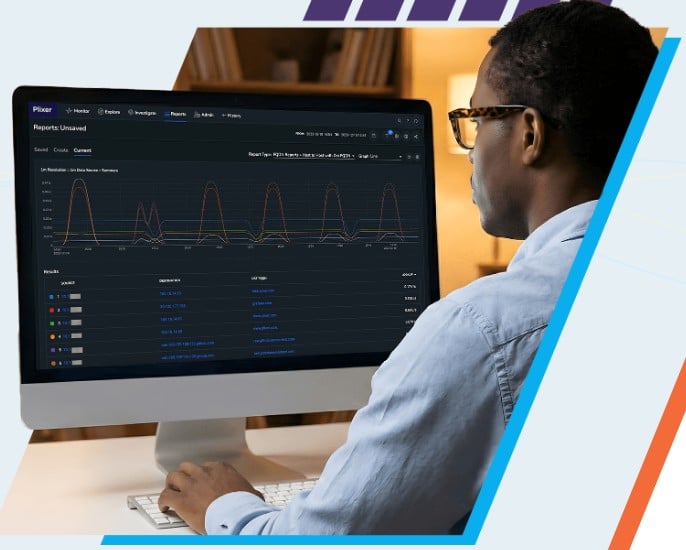
FlowPro inspects DNS activity directly from network traffic using deep packet inspection. It evaluates both DNS requests and responses to identify behavioral patterns and protocol-level anomalies that traditional logging methods often miss.
By analyzing traffic at the packet level, FlowPro captures context that is not available in standard DNS logs, providing more accurate visibility into how domains are being queried, resolved, and used across the network.
Why choose Plixer FlowPro?
- Application performance monitoring — combines flow-based analysis with deep packet inspection to reveal application latency, throughput, packet loss, retransmissions and round-trip time per connection, isolating faults to systems, network paths, subnets or users.
- DNS threat detection — real-time analysis of queries and responses surfaces NXDOMAIN bursts, DGA domains, DNS tunnelling and data exfiltration that standard DNS logs miss.
- Deep packet inspection — captures packet-level context, not just flow-level metadata, for more accurate visibility into how domains are queried, resolved and used.
- Selective, event-driven packet capture — activates automatically when anomalies are detected, minimises PCAP storage requirements, and exports directly to forensic tools such as Wireshark.
- Encrypted traffic visibility — JA3/TLS fingerprinting and FQDN extraction reveal threat behaviour inside encrypted sessions without decryption.
- Threat feeds and custom rules — Suricata-based custom NIDS rules plus threat feed and domain reputation integration, with configurable whitelists and blacklists.
- Enterprise-wide correlation — enriched data forwards to Plixer One and Scrutinizer, so distributed sensors in segmented or multi-site zones still feed a centralised view.
- Flexible deployment — rack-mountable hardware appliance or software deployable in a hypervisor (ESXi, Hyper-V, KVM).
Technical specification
-
PlatformPlixer FlowPro — an advanced packet metadata generator using deep packet inspection for application performance monitoring, DNS analytics and threat detection
-
Subscription term3-year subscription, billed annually — this listing covers Year 1
-
Deployment methodPassive monitoring via TAP, SPAN or mirror port (ERSPAN supported) — monitors mirrored traffic without touching the original packets, so it can be deployed where devices can't natively export flow data
-
Application performance monitoringFlow-based analysis combined with deep packet inspection reveals packet loss, retransmissions, round-trip time, application latency, throughput and server performance per connection, for internal or cloud-bound traffic
-
DNS analyticsReal-time inspection of DNS requests and responses; detects NXDOMAIN bursts, irregular TXT record usage, malformed responses and abnormal query structures against a learned baseline of normal activity
-
Threat detectionIdentifies DNS tunnelling, data exfiltration, algorithmically generated domains (DGAs), botnet activity, command-and-control beaconing and phishing infrastructure from domain behaviour and query timing
-
Encrypted traffic visibilityJA3/TLS fingerprinting and FQDN extraction give visibility into encrypted sessions without decryption
-
Selective packet captureEvent-driven capture activates only when anomalies are detected, minimising PCAP storage requirements; captured packets export to forensic tools such as Wireshark
-
Rule engine & threat feedsSuricata-based custom NIDS rules covering unusual protocol usage, unexpected flow patterns, file transactions/extractions and other anomalies, plus threat feed and domain reputation integration with configurable whitelists and blacklists
-
Data outputEnriched flow metadata forwarded to Plixer One / Scrutinizer for enterprise-wide correlation, with pre-defined and custom report generation
-
Deployment optionsRack-mountable hardware appliance, or software deployable in a hypervisor (VMware ESXi, Hyper-V or KVM); distributed sensors supported for multi-site deployments; additional storage configurations available on request
-
Minimum system requirements1 CPU with 2 cores at 2.0GHz+, 2GB RAM, 5GB storage and ESXi 5.0 or newer
-
Typical use casesApplication performance troubleshooting (packet loss, latency, throughput); DNS compromise risk (hijacking, cache poisoning, resolution disruption); VoIP/phone QoS monitoring (ToS, packet loss, jitter, codec usage); rule-based intrusion detection (botnet, C2, encryption anomalies); encrypted traffic analysis without decryption; deep packet inspection for forensic investigation via Wireshark
Let's talk
Contact us Today
Copyright © 2026 Info Stor Limited. All rights reserved. E & OE. Registered in England and Wales Number 06621886
Registered Office: 6th Floor, 9 Appold Street, London EC2A 2AP, United Kingdom. VAT number: 934 4316 30. D-U-N-S® Number: 211273713.